
Last night if you visited this site (NZ time) you would have seen this:
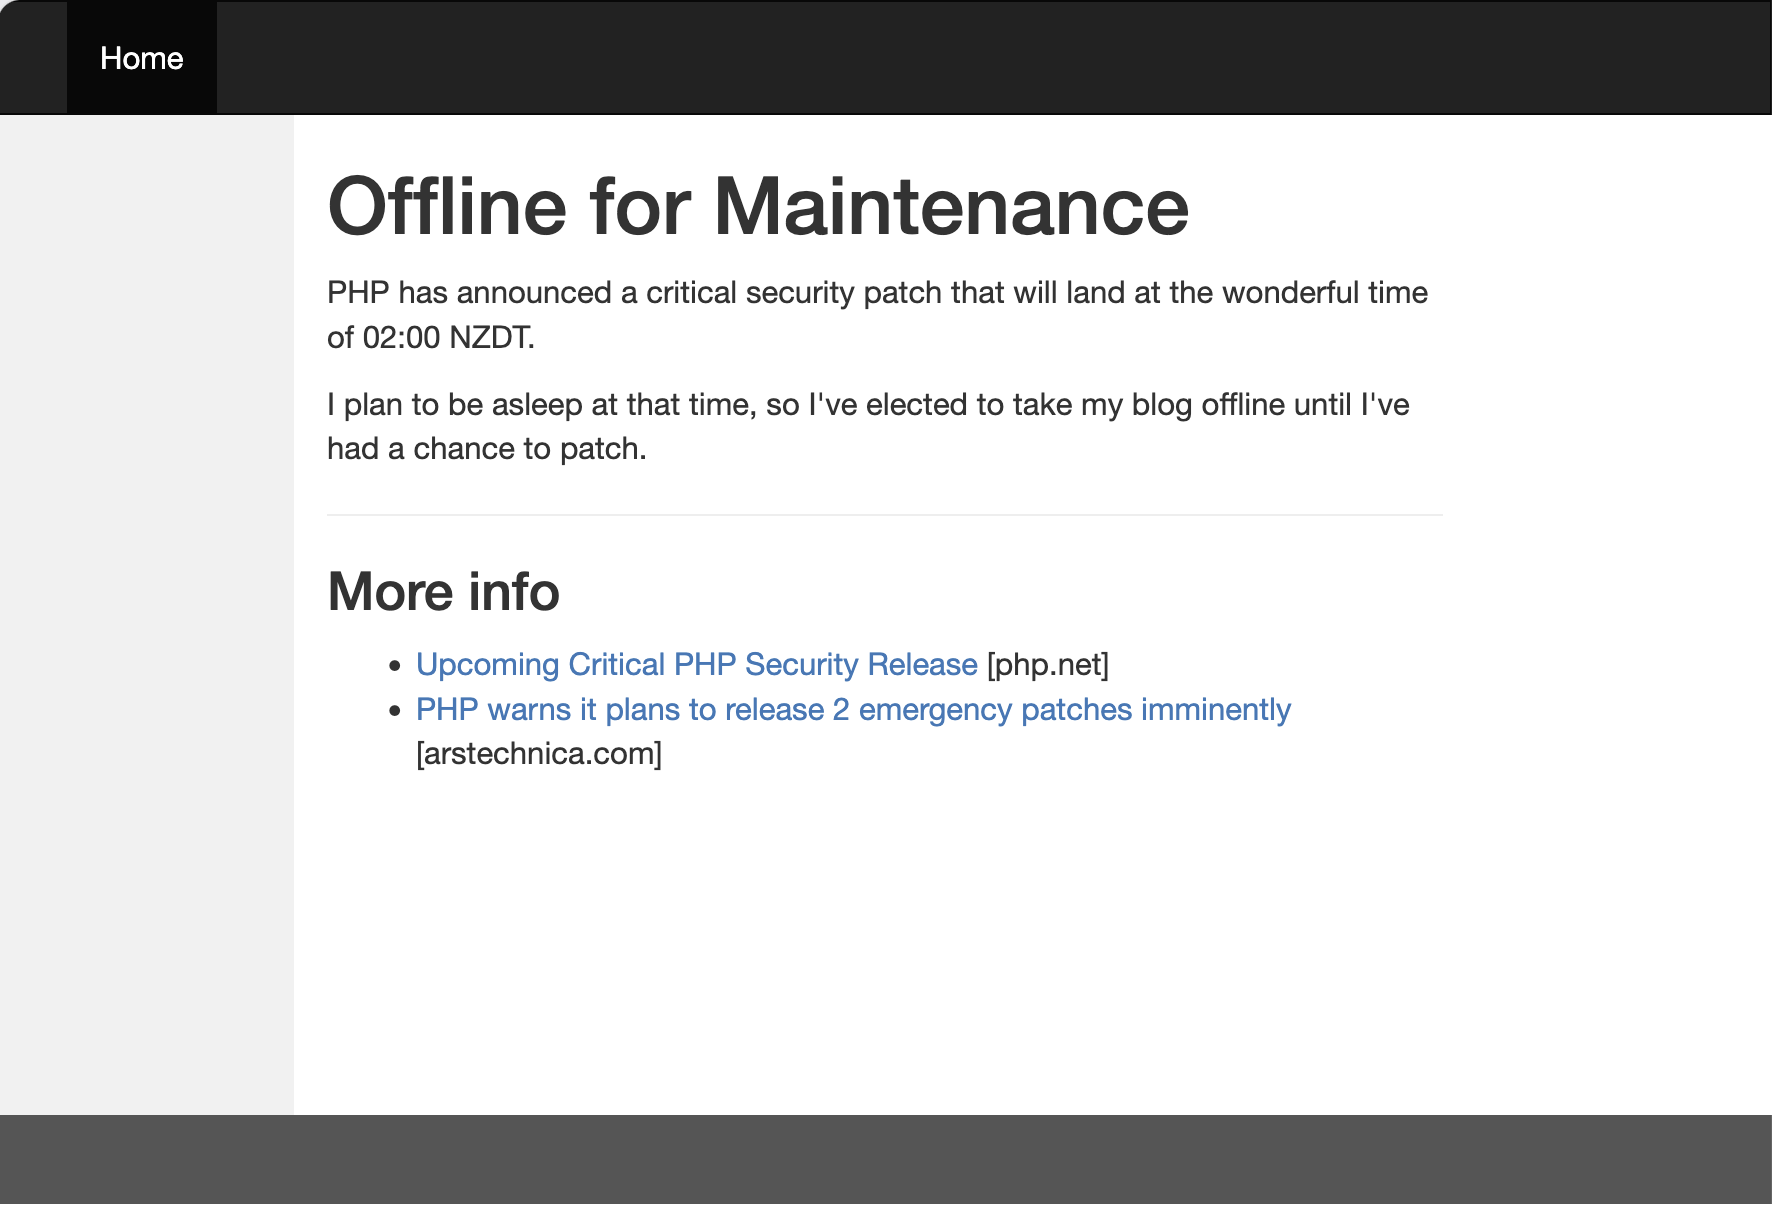
This was because PHP gave advance warning of a critical security vulnerability, with the fix landing at 2am NZDT, when I was asleep.
Setting this up was fortunately very easy – I simply replaced the WordPress Docker container with an nginx container that mounted a basic redirect-to-root nginx config and a single index.html page to the right places, and anyone that visited the site would have seen the above.
The nginx config:
worker_processes  1;

events {
    worker_connections  128;
}

http {
    include       mime.types;
    default_type  application/octet-stream;

    keepalive_timeout  65;

    server {
        listen 80;
        server_name  blog.al4.co.nz;

        root /usr/share/nginx/html;
        index index.html;
        rewrite ^\/.+$ /index.html last;

        location / {
        }
    }
}
The wordpress container in the Docker Compose file was then swapped out by replacing it with:
  wordpress:
    # maintenance mode
    image: nginx:alpine
    expose:
      - 80
    volumes:
      - /host/path/to/index.html:/usr/share/nginx/html/index.html
      - /host/path/to/nginx.conf:/etc/nginx/nginx.conf
    restart: always
    networks:
      - frontend
Taking the whole site offline isn’t ideal, but this does seem to be the reality of hosting a dynamic website these days. Maybe it’s time to look at migrating to a static site generator again.
This blog doesn’t get a lot of traffic (mostly older posts and a few AI bots scraping), not helped by my lack of posting, so I’m sure very few (if any) real people were affected.