Last night if you visited this site (NZ time) you would have seen this:
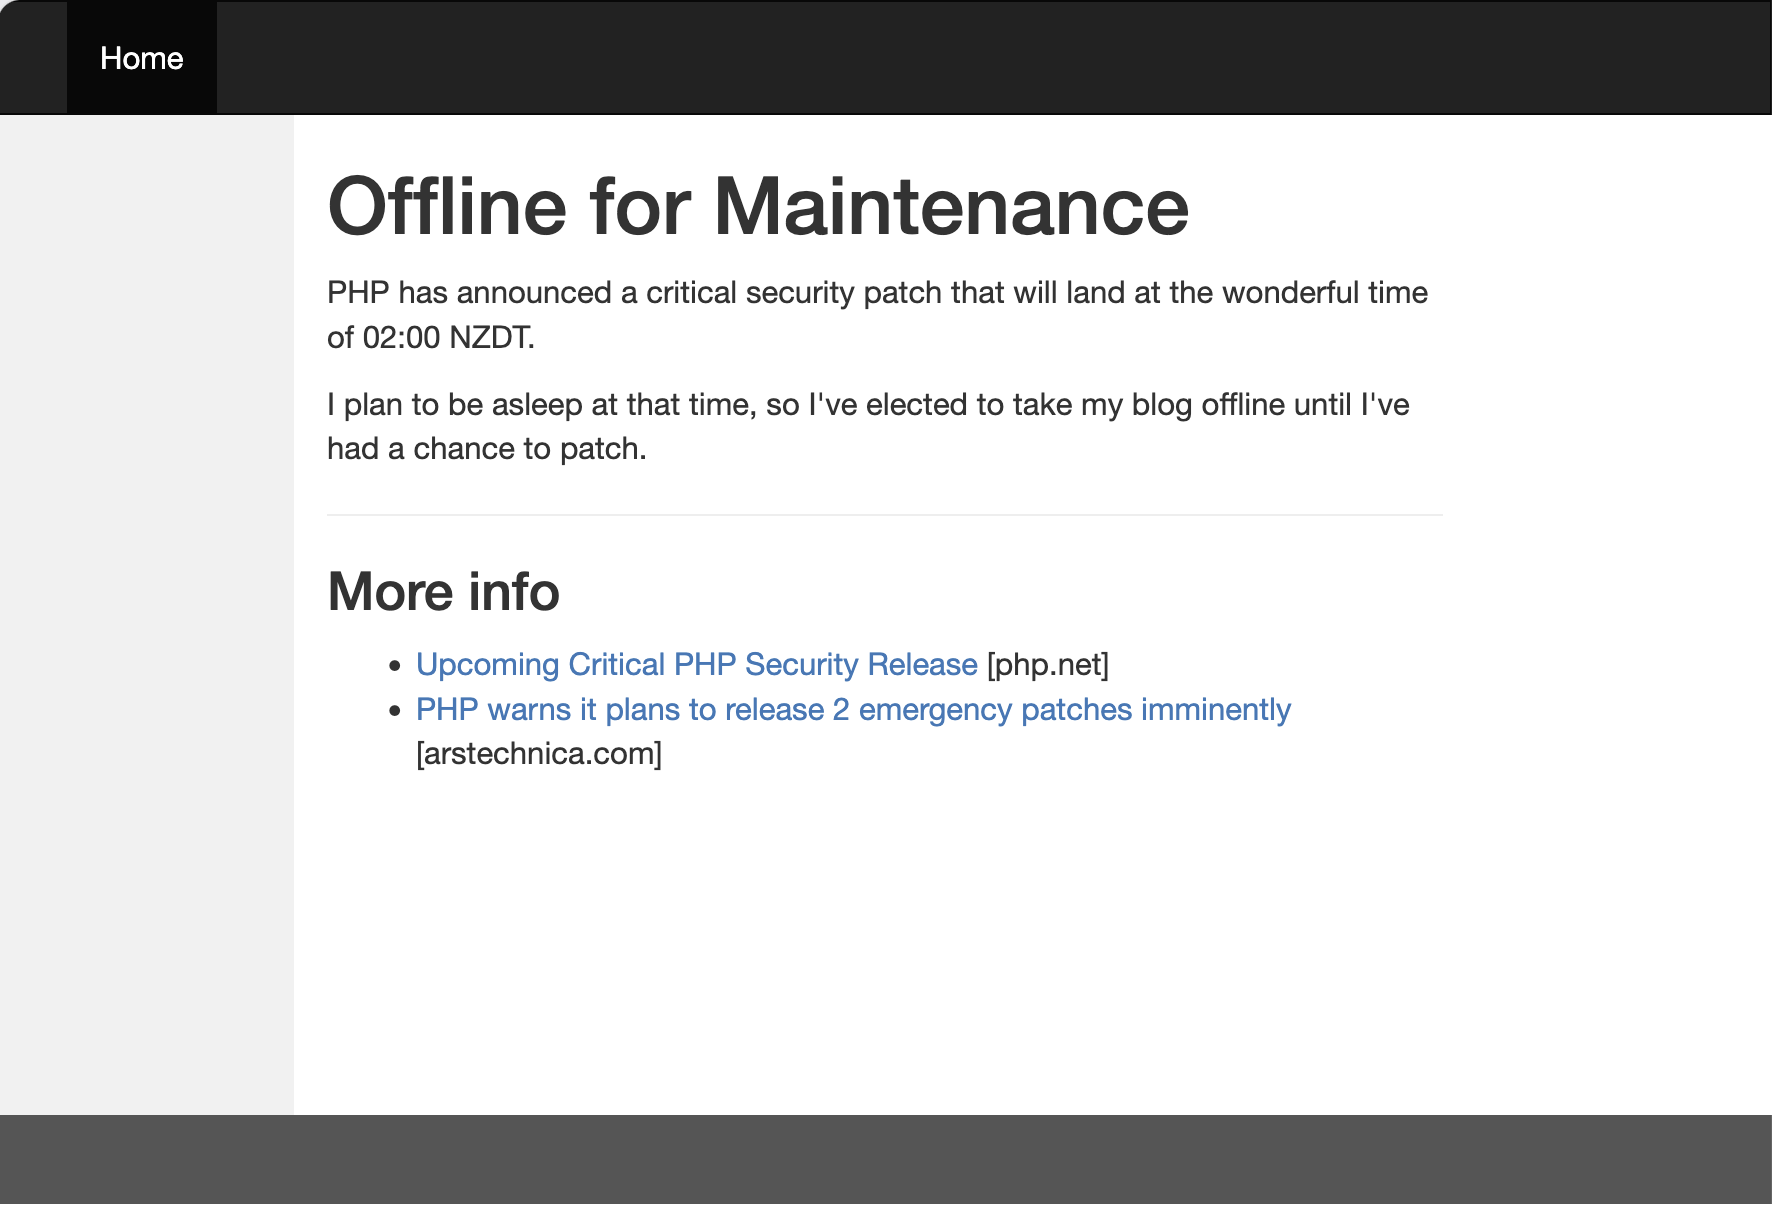
This was because PHP gave advance warning of a critical security vulnerability, with the fix landing at 2am NZDT, when I was asleep.
Continue reading
Last night if you visited this site (NZ time) you would have seen this:
This was because PHP gave advance warning of a critical security vulnerability, with the fix landing at 2am NZDT, when I was asleep.
Continue readingMy experience running IT infrastructure at home, with some recommendations for
anyone starting out on their Homelab journey.
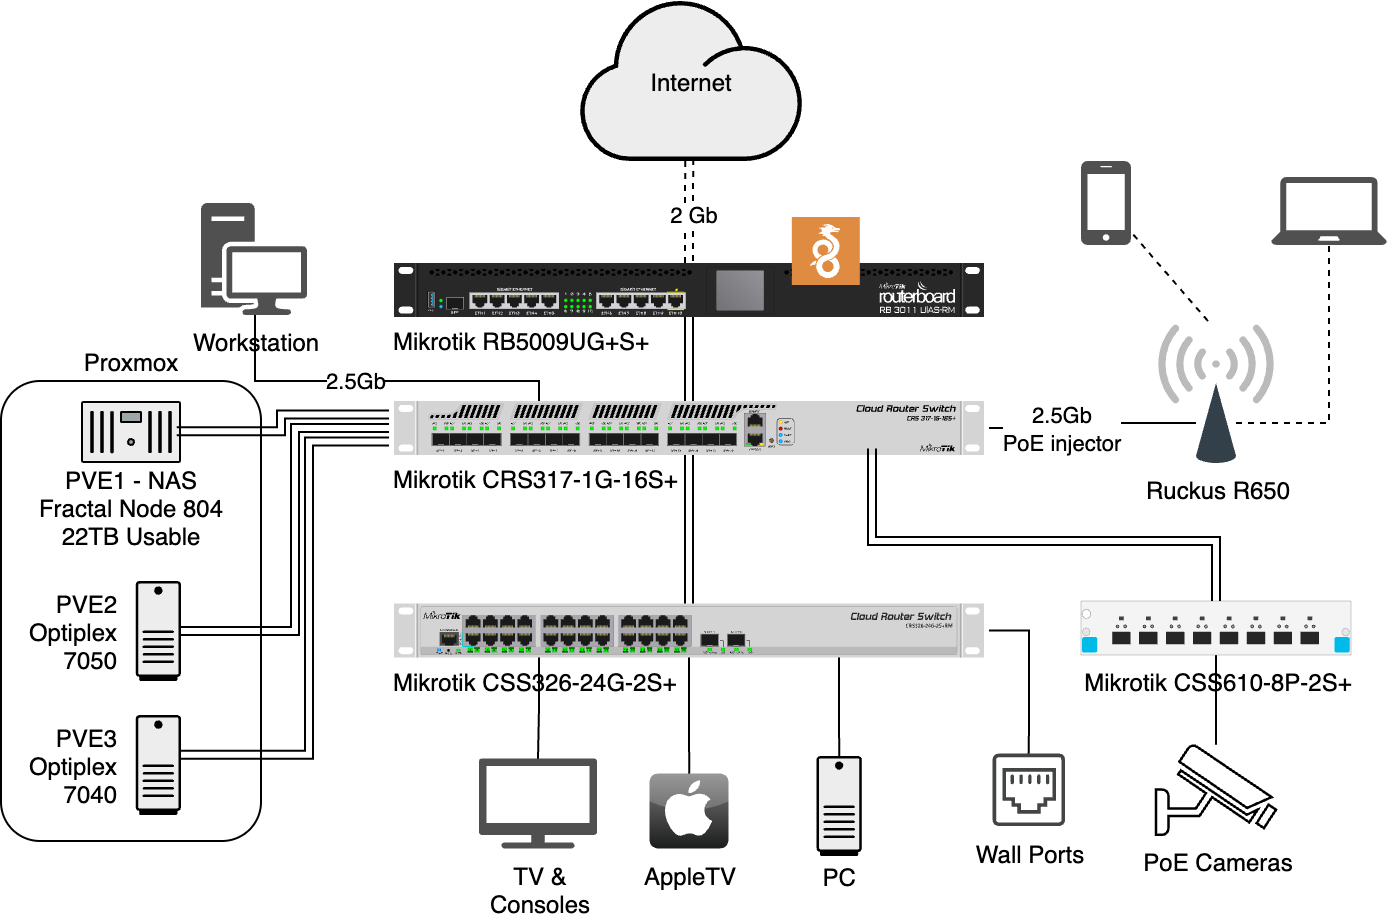
I’ve been running a home server of some kind for more than 20 years. It started when I was at university, hosting a website on an old PC to share party photos (this was in the days before social media). It worked, but was madness in hindsight. The intent wasn’t to make the photos public (it was password-protected), but I was publishing PHP applications (Drupal and Gallery) on the public internet with a “make it work” Apache configuration, whilst being blissfully ignorant of the security risks. That code running today would be compromised in seconds.
Since I left university, all my home servers have been lan-facing only – no external ports. My approach has always been fairly minimalist, mainly because I’ve moved around a lot and never had the spare space to keep lots of IT hardware. I went from flatting in Christchurch, to flatting in Auckland, to living in London where space is at a premium. It’s only in the past year that we’ve brought a house and I’ve been able to consider a more expansive setup. However playing with enterprise hardware doesn’t excite me the way it used to, so I lean heavily towards the quiet and energy efficient, which for the most part means lower-power enthusiast-grade gear.
Of course those that know me would scoff at calling my setup minimalist, because by the standards of normal people it’s anything but. I have 3 rack-mounted switches (all connected with 10Gb uplinks), 3 PCs cosplaying as servers, a router and an ex-enterprise wireless access point all sitting on the “coms shelf”. Most people just have the WiFi router their ISP supplied, plus a couple of laptops, phones and maybe a desktop in the office.
It wasn’t always this way though, my home network has evolved over the years, and will no doubt continue to do so. So consider this a snapshot in time of my personal learning.
Continue reading1. Anything that is in the world when you’re born is normal and ordinary and is just a natural part of the way the world works.
Douglas Adams, The Salmon of Doubt
2. Anything that’s invented between when you’re fifteen and thirty-five is new and exciting and revolutionary and you can probably get a career in it.
3. Anything invented after you’re thirty-five is against the natural order of things.”
It’s commonly known that younger generations tend to be more enthusiastic adopters of new technology. It’s easy to see why – younger people are more hungry to learn, are still forming habits, and have more to gain (and less to lose) from technological revolution.
So it’s worth casting my own resistance to crypto through this lens. I have always been an enthusiastic adopter of the internet and technology, and that attitude has served me very well; I owe my livelihood to it. It would be easy for me to jump on the Web3 bandwagon and go all-in on crypto.
Or would it?
Continue readingBecause the captains did a while ago.
Exhibit A – the github activity graph for the keybase client:
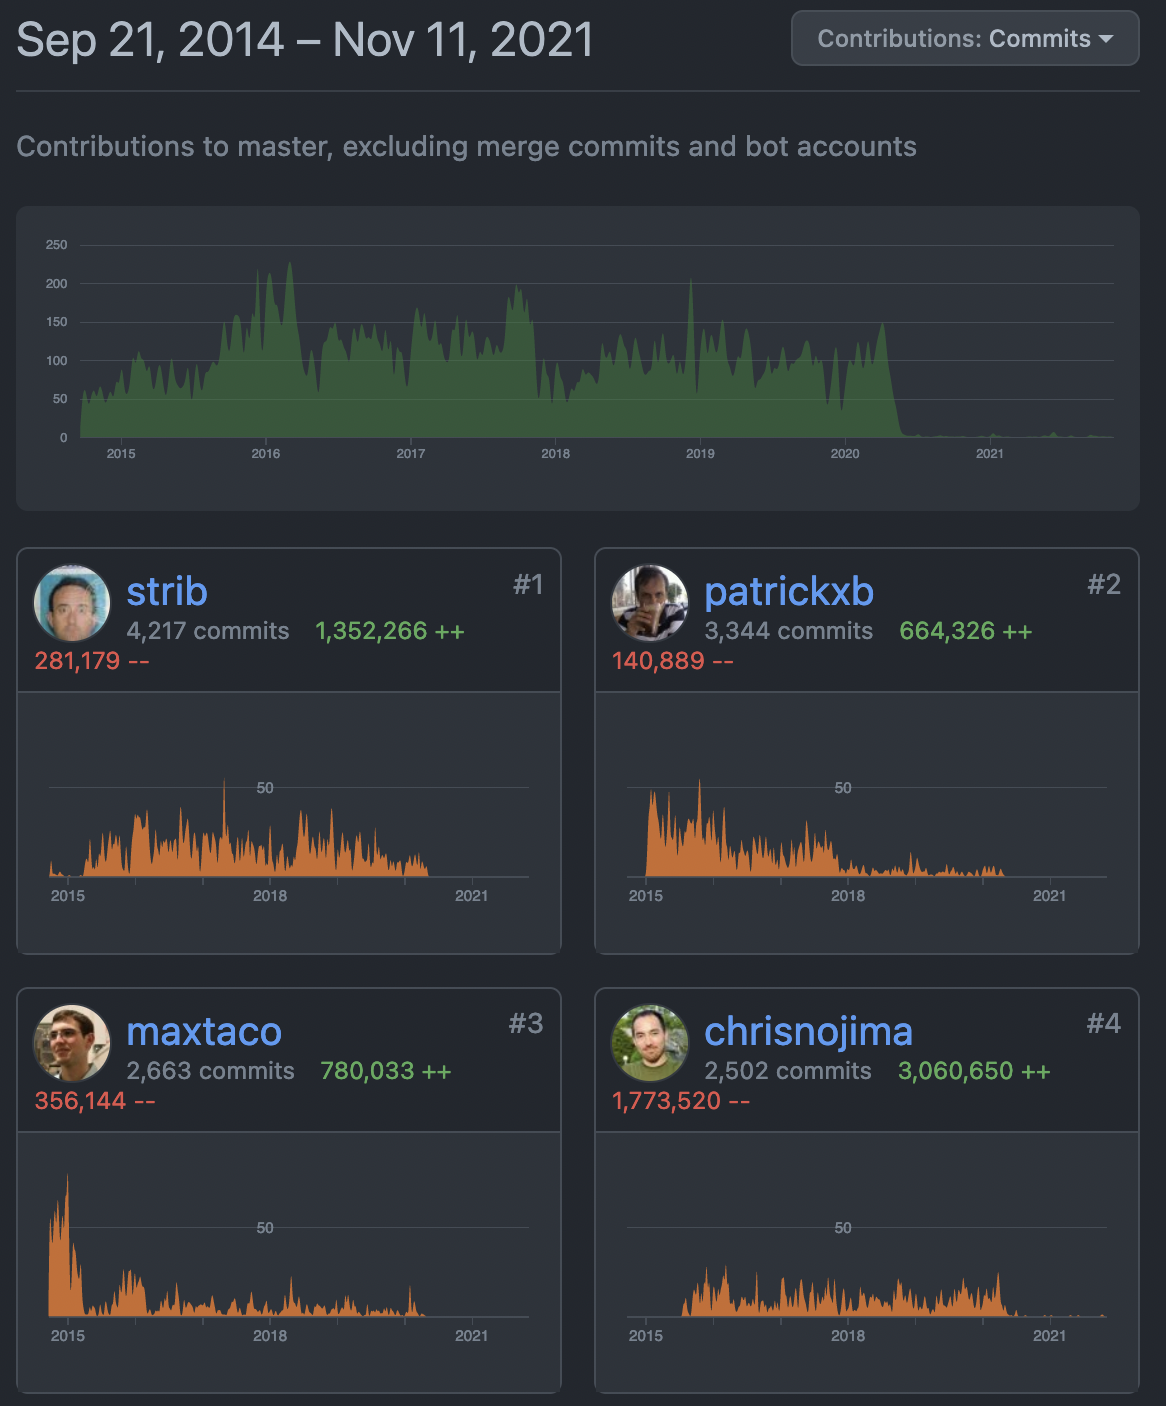
Development basically ceased in 2020 when the team joined Zoom.
This means no further improvements, including support for Apple Silicon.
This was a skills acquisition for Zoom no doubt – they needed the talent after they were taken to task over the state of their security before the pandemic. I’m sure the Keybase team has made a huge contribution to their product. But I highly doubt they have any commercial interest in continuing the Keybase project.
I’ll miss the encrypted git feature. And the Stellar Lumen giveaway was neat. But every problem it solved for me is easily solved with other tools today.
Au revoir.
Our company uses Perkbox as an employee benefits program. It has some nice freebies, but on the whole I find it’s mostly marketing – I.E. “benefits” that make little sense except as paid promotions.
So while I was happy to see a “get a case of craft beers delivered free” as one of the employee perks, I was fairly skeptical going in…
The catch is that you have to sign up to monthly deliveries from Beer52 which are very much not free. Not free, to the tune of £24 per month. And that’s a pretty price to pay for 8 beers.
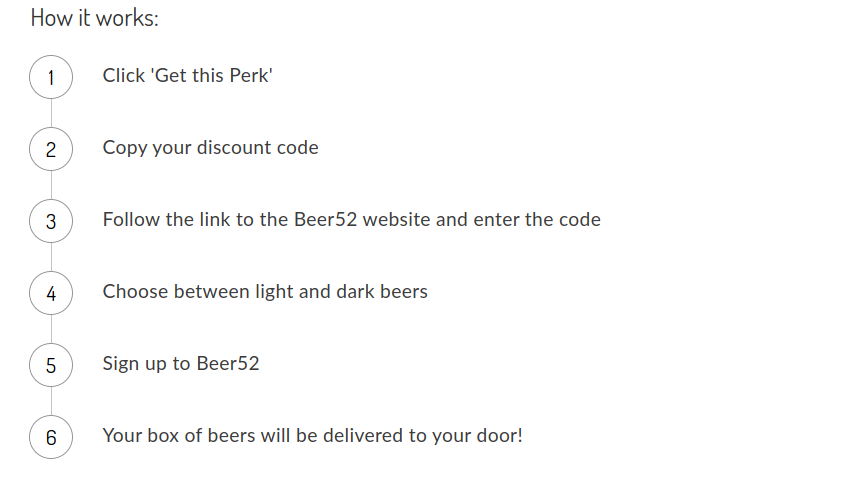
I didn’t want to be “that guy” who just orders the free case and cancels, so I decided to let it run for another month and cancel after. But of course I ended up letting it run for about 5 months, because, hey, it’s beer! But when I did decide to cancel, I found a cancellation process designed to be as sticky as possible.
Firstly – you can’t cancel until the first box is delivered. OK, fair enough I guess.
Secondly – you can’t cancel online. You can do everything else – order beer, pause your subscription for a month, switch to 2-monthly deliveries, update payment details, all the usual stuff. Except cancel, of course.
Nope, to cancel you have to phone them up, sit in the hold queue (it took 15 mins for me), answer a question on why you want to leave, listen to two offers (I was offered an £8 discount on the next box in exchange for not cancelling), and only then will they cancel your subscription for you.
In doing so they hope you’ll carry on paying £24/month after the discounted one, just like you did after the free one.
Sign up with a “free case” code. Log in. Switch to 2 or 3-monthly deliveries. Skip the next one. All this can be done online as soon as you’re signed up.
That way you won’t be automatically paying for a case for about 3 months, which is plenty of time to cancel if you just want the free box. And if you want more, you can order an extra case at any time, which is better than having it sprung on you when you don’t.
There is no reason for it, other than customer retention. Retention, of customers that would rather not spend their money on your product.
Don’t feel bad about canceling after the free case.
The last time I upgraded my laptop, I went from a Dell Latitude E4300, to a late-2013 13″ Macbook Pro. That was six years ago!
I didn’t expect to get anywhere near 6 years from the mac, as it’s not exactly upgradeable (you can replace the SSD, but that’s it). Modern macbooks are even worse – even the SSDs are soldered. Thus, you’d better anticipate your needs over the lifetime of the machine, because once you click buy, that’s the specification it will have for life.
The Latitude E4300 I had before it lasted 5 years, which was also very good. Back then, laptop technology was improving noticeably with each generation, but it’s fair to say that Intel’s dominance and complacency in the x86 CPU market resulted in marginal gains between generations. You could skip 3 generations and barely notice a performance increase.
Fortunately things have now changed. AMD’s release of its Ryzen processors a couple of years ago gave Intel a much-needed kick, and now we suddenly have 4 and 6-core designs in 15W power envelopes. The improvements over Sandy Bridge and Haswell are now substantial and easily warrant an upgrade.
Thus, the Macbook is starting to feel slow. It’s specs are:
8GB of ram is what I’d consider the bare minimum – acceptable for browsing but not really software development or content creation. The 512GB SSD is still serviceable, but at ~700MB/s read and write, it is rather slow compared to modern NVME drives which can top 3,000MB/s in ideal conditions. But the performance of the 28W dual-core i5 is probably what’s driving this upgrade the most.
So in late-2019 I started shopping for a new portable laptop to replace the macbook. My requirements are:
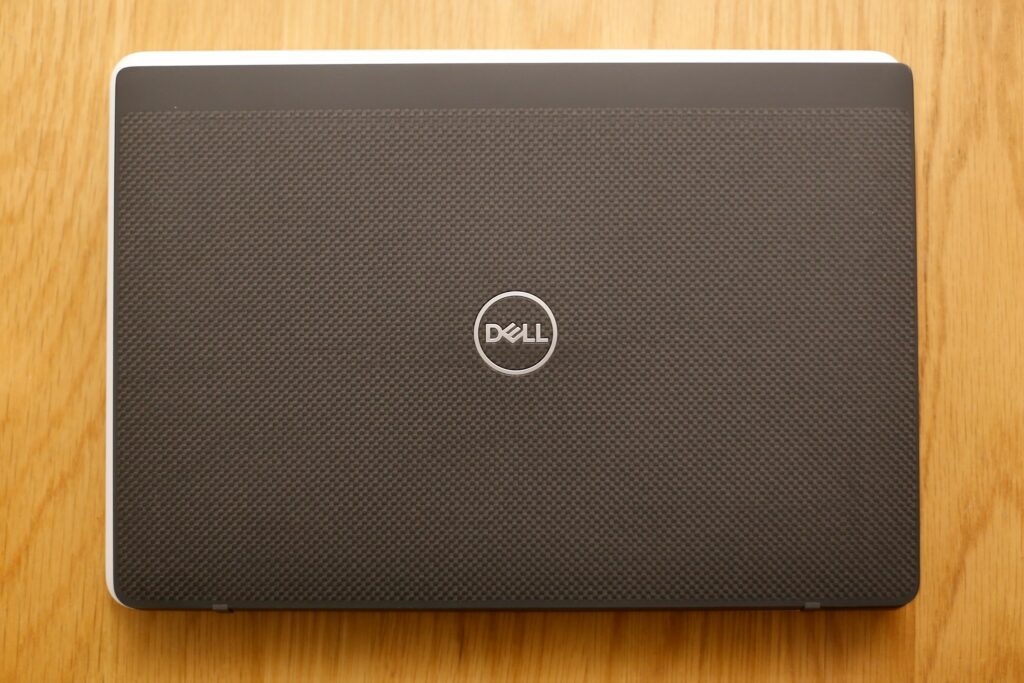
To cut a long story short, this time around I have gone back to the future and bought a Dell Latitude instead of another Mac.
Continue readingAt work we have a very large and highly active repository which contains the majority of our company’s code. Despite regular pruning and garbage collection, this repo can get rather slow, and the asynchronous git commands run by zprezto often get in the way of actual work, like commits, by holding locks at inopportune times.
Thus, selectively disabling the git prompt for some repositories makes a lot of sense, as the cost outweighs the benefit if it’s constantly getting in the way.
I couldn’t find direct instructions for doing this online, but fortunately the code is easy to parse; there’s a check for a git config option here.
As git configuration can be on a per-repository basis, all you need to do is run the following command from your giant repo to disable the git prompt:
git config --bool prompt.showinfo falseAnd you’ll still see the git status information on other repositories without this config option.
Note, this will obviously work only for themes that use the built-in git module, but that should be most of them.
This surprised me, but it’s there in black and white on the website.
FlexPlus is Nationwide’s premium paid-for current account. For a fee of £10, which increased to £13 in 2017, you got mobile phone insurance, travel insurance, no-fee ATM withdrawals overseas, and 3% interest on balances up to £2,500. It’s been MoneySavingExpert’s recommended premium account for years now, and until recently was a great deal. Possibly a bit too good to be true.
Continue readingA while ago I wrote a post about my backup solution and replacing Crashplan – a once great product I was a happy user of. It served pretty much all my backup needs in one product, but alas it was too good to last.
Eventually I settled on Duplicati on my home server backing up to Backblaze, and Urbackup to back up my various devices to the NAS. But since then a few things have changed:
Er, yeah. Despite writing “I think that you should never use Dropbox for anything remotely private or sensitive”, words that I stand by today, I have not only been using Dropbox… but for private and sensitive things.
Continue readingToday I read an article on Arstechnica (Right-wingers say Twitter’s “bias” against them should be illegal), and, as hot-button political topics such as this so often do, it spawned an interesting comment thread. Ars is a thoughtful, rational, and evidence-based site, so it should come as no surprise that the majority of commenters are of the same persuasion. So much so that the comment threads are occasionally more interesting than the original article.
The argument you often hear from the far right, is that refusing to publish or listen to their hate-speech amounts to censorship. By “censoring” their speech, the supposedly “tolerant” society is behaving like the Third Reich. Godwin’s law aside, this latest attempt by Trump and Co. to stop Twitter and other social media companies “silencing conservative voices”, runs along similar lines; they are arguing that bias in suppressing “conservative voices” should be illegal, in the name of free speech.
Continue reading